|
|
|
|
|
|
| |
| |
|
|
|
|
| |
| |
|
|
OK, so on the basis that somebody here might already know the answer to
this one...

I want to give certain users the power to stop and restart a specific
service at will. I can do this by adding them to the local
Administrators group - however, that would *also* give them the power to
log other users off of the PC, which I don't want. Is there some way to
allow them to control this service, but *not* allow them to kick people
off the PC?

Also, just for your amusement: The PCs in question run Windows NT 4.0
SP6a. >_<
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Invisible wrote:
> Also, just for your amusement: The PCs in question run Windows NT 4.0
> SP6a. >_<

Thoughts:

See if the service will run in a different group, or whether it needs to
have some sort of admin privs. Then give someone privileges to log in as
that group and control the service that way.

See if there's something in Group Policy that lists a specific stop/start
privilege for services. I'm talking under the "user rights assignment" table.

Third, write a "set uid" program and give it rights to impersonate the
administrator to start or stop the service.

Worse comes to worst, write a kludge program that runs all the time in the
administrators group and watches for a "start.txt" or "stop.txt" to be
created in a particular directory, then invokes the appropriate "net start"
and "net stop" commands. Note this solution takes no particular knowledge of
windows APIs and can be regulated just by giving whoever you want the
appropriate permissions on the appropriate directory.


--
   Darren New, San Diego CA, USA (PST)
   The NFL should go international. I'd pay to
   see the Detroit Lions vs the Roman Catholics.
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Darren New wrote:

> Thoughts:
>
> See if the service will run in a different group, or whether it needs to
> have some sort of admin privs. Then give someone privileges to log in as
> that group and control the service that way.
>
> See if there's something in Group Policy that lists a specific
> stop/start privilege for services. I'm talking under the "user rights
> assignment" table.
>
> Third, write a "set uid" program and give it rights to impersonate the
> administrator to start or stop the service.
>
> Worse comes to worst, write a kludge program that runs all the time in
> the administrators group and watches for a "start.txt" or "stop.txt" to
> be created in a particular directory, then invokes the appropriate "net
> start" and "net stop" commands. Note this solution takes no particular
> knowledge of windows APIs and can be regulated just by giving whoever
> you want the appropriate permissions on the appropriate directory.

Doing some research, apparently it's not just files that can have
permissions. Registry keys, services, printers (??!) and so forth can
all have ACLs attached to them.

Not that you'd know that from the UI. :-P

Anyway, apparently Process Explorer has the power to show _and edit_ the
ACLs associated with a running service. (It's unclear whether it changes
the security token on the running process, or actually changes the
service configuration so that it will have the new security *every* time
it's run.)

Unfortunately, although this appears to work fine on Windows XP... [I'm
sure you see where I'm going with this.]

There's no huge problem with everybody having administrative rights over
the local machine, expect... that allows you to forcibly log other
people off the machine. Which would be "bad".

And now I'm wondering... maybe it's a "right" you can set? (As you may
remember, permissions apply to resources, rights apply to users.) I
wonder if I can either assign the "stop service" right to a user group,
or else create a mini-admins group and somehow revoke the "kick people
off" right?...

Otherwise, yeah, I'm going to end up writing some horribly hackish
script to kill and restart this damned service. :-(

--
http://blog.orphi.me.uk/
http://www.zazzle.com/MathematicalOrchid*
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Orchid XP v8 wrote:
> Doing some research, apparently it's not just files that can have
> permissions. Registry keys, services, printers (??!) and so forth can
> all have ACLs attached to them.
>
> Not that you'd know that from the UI. :-P

Huh...

Printer: http://i.techrepublic.com.com/gallery/60654-474-477.jpg
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
[stupid Ctrl-Enter sending message immediately]

Nicolas Alvarez wrote:
> Orchid XP v8 wrote:
>> Doing some research, apparently it's not just files that can have
>> permissions. Registry keys, services, printers (??!) and so forth can
>> all have ACLs attached to them.
>>
>> Not that you'd know that from the UI. :-P
>
> Huh...
>
> Printer: http://i.techrepublic.com.com/gallery/60654-474-477.jpg
http://tinyurl.com/6xqhbr

Registry key:
http://www.eisenschmidt.com/jweisen/misc/lawson/registry_permissions.jpg
http://www.oucs.ox.ac.uk/viruses/itss/regpermissions.png

Service:
http://blog.binaryfactory.ca/wp-content/uploads/2008/05/gpodefault.jpg

Share:
http://www.get-digital-help.com/permissions-recorded-tv.png

Exchange mailbox:
http://tinyurl.com/6m4ere

etc
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Orchid XP v8 wrote:
> Doing some research, apparently it's not just files that can have
> permissions. Registry keys, services, printers (??!) and so forth can
> all have ACLs attached to them.

Um, sure. I hadn't heard of it with services, but the registry editor and
the printers both have property pages for security just like files do. You
might need to invoke regedt32 instead of regedit to get the version that has
the security stuff, IIRC.

And yes, everything has ACLs attached, including all your devices,
processes, connections, etc etc etc. Everything you can name in the kernel
has ACLs on it.

> Not that you'd know that from the UI. :-P
>
> Anyway, apparently Process Explorer has the power to show _and edit_ the
> ACLs associated with a running service. (It's unclear whether it changes
> the security token on the running process, or actually changes the
> service configuration so that it will have the new security *every* time
> it's run.)

It changes it next time it runs, if you change it from the service
configuration screens. (You know, the same set of tabs that shows you what
other services and stuff it depends on, not the "task manager"-like stuff. I
don't know which PE you're using there.)

I never tried setting up a service running as Fred and then had Fred try to
stop just that one. If that works, that would seem to be the way to go, if
you can.

> Unfortunately, although this appears to work fine on Windows XP... [I'm
> sure you see where I'm going with this.]
>
> There's no huge problem with everybody having administrative rights over
> the local machine, expect... that allows you to forcibly log other
> people off the machine. Which would be "bad".
>
> And now I'm wondering... maybe it's a "right" you can set?

That was my second suggestion. It'll likely be in the "user rights
assignment" list if it is. Maybe domain controllers have more of this sort
of thing than the individuals?

> Otherwise, yeah, I'm going to end up writing some horribly hackish
> script to kill and restart this damned service. :-(

It's that, or learning some deep Windows juju to invoke the LoginUser API to
change your own ownership when the program runs. Maybe you could have a "run
as" script?

Does this help?
http://www.codeguru.com/cpp/w-p/system/article.php/c5755
At least someone else wrote the hacky script for you. :-)


--
   Darren New, San Diego CA, USA (PST)
   The NFL should go international. I'd pay to
   see the Detroit Lions vs the Roman Catholics.
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Nicolas Alvarez wrote:
>> Not that you'd know that from the UI. :-P
> Printer: http://i.techrepublic.com.com/gallery/60654-474-477.jpg

And as long as we're pointing out the obvious... :-)

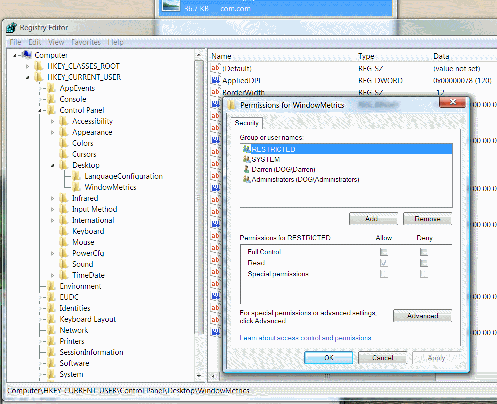
This is from Vista. I think you need regedt32 to get the "permissions" tab
under pre-XP systems.

--
   Darren New, San Diego CA, USA (PST)
   The NFL should go international. I'd pay to
   see the Detroit Lions vs the Roman Catholics.
Post a reply to this message
Attachments:
Download 'image1.gif' (37 KB)
Preview of image 'image1.gif'
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Nicolas Alvarez wrote:
> Service:
> http://blog.binaryfactory.ca/wp-content/uploads/2008/05/gpodefault.jpg

Hmmm... Where did you get that page from? It's not in my interface anywhere
obvious. Are you sure that's not specific to the print spooler?

--
   Darren New, San Diego CA, USA (PST)
   The NFL should go international. I'd pay to
   see the Detroit Lions vs the Roman Catholics.
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
http://support.microsoft.com/kb/256345/EN-US/

That says Windows 2000, but it might be similar on NT?

--
   Darren New, San Diego CA, USA (PST)
   The NFL should go international. I'd pay to
   see the Detroit Lions vs the Roman Catholics.
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
>> Doing some research, apparently it's not just files that can have
>> permissions. Registry keys, services, printers (??!) and so forth can
>> all have ACLs attached to them.
>>
>> Not that you'd know that from the UI. :-P
>
> Huh...
>
> Printer: http://i.techrepublic.com.com/gallery/60654-474-477.jpg

It's reasonably easy to overlook though. :-P

--
http://blog.orphi.me.uk/
http://www.zazzle.com/MathematicalOrchid*
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Nicolas Alvarez wrote:

> http://tinyurl.com/6xqhbr

Yeah, it's tucked away in there, but it's not "hard" to find if you
realise it exists and you go look for it.

> Registry key:

Very easy to overlook. But then, raw registry editing demands knowledge
and caution anyway! o_O

> Service:
> http://blog.binaryfactory.ca/wp-content/uploads/2008/05/gpodefault.jpg

Riiiight. And, as you obviously realise, the article this is from is
describing how to apply security to services using a *Group Policy*.
And, as you also know, Group Policies DO NOT WORK WITH NT. :-P

http://blog.binaryfactory.ca/2008/05/windows-service-permissions-concerns-when-hardening-servers/

Now, Mr Smarty, if you know how to actually do this *in Windows NT*,
_then_ I'll be impressed. Cos I've spent all ****ing day trying to find
it. :-(

> Share:
> http://www.get-digital-help.com/permissions-recorded-tv.png

Yeah, everybody knows about files and shares.

> Exchange mailbox:
> http://tinyurl.com/6m4ere

I don't even have access to *touch* our Exhange system...


You didn't show the UI for changing the ACLs on running processes. :-P

--
http://blog.orphi.me.uk/
http://www.zazzle.com/MathematicalOrchid*
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Darren New wrote:
> Nicolas Alvarez wrote:
>> Service:
>> http://blog.binaryfactory.ca/wp-content/uploads/2008/05/gpodefault.jpg
>
> Hmmm... Where did you get that page from? It's not in my interface
> anywhere obvious. Are you sure that's not specific to the print spooler?

It's a Group Policy setting. You won't find it in the Settings applet on
the Control Panel.

http://blog.binaryfactory.ca/2008/05/windows-service-permissions-concerns-when-hardening-servers/

--
http://blog.orphi.me.uk/
http://www.zazzle.com/MathematicalOrchid*
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Darren New wrote:

> And as long as we're pointing out the obvious... :-)
>
> This is from Vista. I think you need regedt32 to get the "permissions"
> tab under pre-XP systems.

Yes, I found that some time ago.

(Some KB article on fixing an obscure glitch in Office 97 due to a
registry key having the wrong permissions... Apparently it was designed
with Windows 95 in mind, which doesn't "have" security.)

--
http://blog.orphi.me.uk/
http://www.zazzle.com/MathematicalOrchid*
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Darren New wrote:

> And yes, everything has ACLs attached, including all your devices,
> processes, connections, etc etc etc. Everything you can name in the
> kernel has ACLs on it.

I wonder... what do the ACLs on a process do? (Not to be confused with
the security tokens the process has. These presumably control what the
*process* is allowed to do, whereas the ACLs control what *you* can do
to that process.)

>> Anyway, apparently Process Explorer has the power to show _and edit_
>> the ACLs associated with a running service. (It's unclear whether it
>> changes the security token on the running process, or actually changes
>> the service configuration so that it will have the new security
>> *every* time it's run.)
>
> It changes it next time it runs, if you change it from the service
> configuration screens. (You know, the same set of tabs that shows you
> what other services and stuff it depends on, not the "task manager"-like
> stuff. I don't know which PE you're using there.)

I hunted around for ages in there. I found the controls to change the
account the service runs under, but nothing to change the ACLs on the
service.

>> And now I'm wondering... maybe it's a "right" you can set?
>
> That was my second suggestion. It'll likely be in the "user rights
> assignment" list if it is. Maybe domain controllers have more of this
> sort of thing than the individuals?

Even in NT, the User Manager thingy has a panel hidden away somewhere
for controlling password expiration times and such, and another next to
it for controlling... well, I forget exactly. But maybe I'll find
something useful in there? I'll take a look tomorrow.

>> Otherwise, yeah, I'm going to end up writing some horribly hackish
>> script to kill and restart this damned service. :-(
>
> It's that, or learning some deep Windows juju to invoke the LoginUser
> API to change your own ownership when the program runs. Maybe you could
> have a "run as" script?

Well, since I know how to program in C++ now, that should be easy! :-D

(I jest. Obviously.)

> Does this help?
> http://www.codeguru.com/cpp/w-p/system/article.php/c5755
> At least someone else wrote the hacky script for you. :-)

Well, that looks like my backup plan...

--
http://blog.orphi.me.uk/
http://www.zazzle.com/MathematicalOrchid*
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Darren New wrote:
> http://support.microsoft.com/kb/256345/EN-US/
>
> That says Windows 2000, but it might be similar on NT?

Group Policy is not supported on NT.

Windows 2000 and higher.

Major PITA, actually...

--
http://blog.orphi.me.uk/
http://www.zazzle.com/MathematicalOrchid*
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Orchid XP v8 wrote:
> It's a Group Policy setting. You won't find it in the Settings applet on
> the Control Panel.

OK. Must be something in the "server" version of the OS that I never had to
administer. All I have is "local policy" tabs.

--
   Darren New, San Diego CA, USA (PST)
   The NFL should go international. I'd pay to
   see the Detroit Lions vs the Roman Catholics.
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Orchid XP v8 wrote:
> I wonder... what do the ACLs on a process do?

Can you debug it? Can you send it a signal? Can a COM object talk to it? Can
you change its priority?

Try starting up the task manager and killing off csrss.exe or the login
process (winlogin.exe?) and see what you get.

> I hunted around for ages in there. I found the controls to change the
> account the service runs under

That's what I was talking about. Sorry I couldn't help.

> Even in NT, the User Manager thingy has a panel hidden away somewhere
> for controlling password expiration times and such, and another next to
> it for controlling... well, I forget exactly. But maybe I'll find
> something useful in there? I'll take a look tomorrow.

Here, it's in CP->Local Security Policy->Local Policies. You probably have
something for group policy management, which I certainly wasn't using back
in NT4 days. :-)

You're thinking of userpassword2.cpl or some such. (userpswd2?) It's not
there, I don't think. That lets you assign users to groups, not rights to
groups.

--
   Darren New, San Diego CA, USA (PST)
   The NFL should go international. I'd pay to
   see the Detroit Lions vs the Roman Catholics.
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Darren New wrote:
> Nicolas Alvarez wrote:
>> Service:
>> http://blog.binaryfactory.ca/wp-content/uploads/2008/05/gpodefault.jpg
>
> Hmmm... Where did you get that page from?

Google Image Search...
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Orchid XP v8 wrote:
> Riiiight. And, as you obviously realise, the article this is from is
> describing how to apply security to services using a *Group Policy*.
> And, as you also know, Group Policies DO NOT WORK WITH NT. :-P
>
>
http://blog.binaryfactory.ca/2008/05/windows-service-permissions-concerns-when-hardening-servers/
>
> Now, Mr Smarty, if you know how to actually do this *in Windows NT*,
> _then_ I'll be impressed. Cos I've spent all ****ing day trying to find
> it. :-(

I have only ever touched group policy in Windows XP.
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
Orchid XP v8 wrote:

> And now I'm wondering... maybe it's a "right" you can set? (As you may
> remember, permissions apply to resources, rights apply to users.) I
> wonder if I can either assign the "stop service" right to a user group,
> or else create a mini-admins group and somehow revoke the "kick people
> off" right?...

Apparently yes.

Apparently anybody who has the "load or unload a device driver" right
can also start and stop system services. (WTF?) So all I need to do is
create a suitable group and assign people to it and I'm done. Yay, me! :-D
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
>> And now I'm wondering... maybe it's a "right" you can set? (As you may
>> remember, permissions apply to resources, rights apply to users.) I
>> wonder if I can either assign the "stop service" right to a user group,
>> or else create a mini-admins group and somehow revoke the "kick people
>> off" right?...
>
> Apparently yes.
>
> Apparently anybody who has the "load or unload a device driver" right can
> also start and stop system services. (WTF?) So all I need to do is create
> a suitable group and assign people to it and I'm done. Yay, me! :-D

If you are worried enough that they will log off other users (either
accidentally or maliciously), then why aren't you worried that they will
start unloading device drivers? ;-)
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
>> Apparently yes.
>>
>> Apparently anybody who has the "load or unload a device driver" right
>> can also start and stop system services. (WTF?) So all I need to do is
>> create a suitable group and assign people to it and I'm done. Yay, me!
>> :-D
>
> If you are worried enough that they will log off other users (either
> accidentally or maliciously), then why aren't you worried that they will
> start unloading device drivers? ;-)

Well, if you do, you only mess your own stuff up. I'm not concerned
about people messing their own stuff up, only other people's stuff! :-D

(Basically, we have a new guy in the lab who is... uh... overly keen to
prove himself. Apparently it's been causing all sorts of problems. This
guy recently discovered that he could kick people off other computers,
and has been doing so extensively. [Not helped by the two morons in
charge of IT accidentally giving everybody at the UK sight administrator
access to every PC on the network - thanks, guys!] So I was told to
"fix" this - which I did. The trouble now is that you can't restart the
service for our flakey lab software, which you need to be able to do...)
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
> This guy recently discovered that he could kick people off other
> computers, and has been doing so extensively.

Geez, what sort of people have you got working there?  Surely that sort of
behaviour demands some sort of official warning, it's not like you're at
school messing about.
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
scott wrote:
>> This guy recently discovered that he could kick people off other
>> computers, and has been doing so extensively.
>
> Geez, what sort of people have you got working there?  Surely that sort
> of behaviour demands some sort of official warning, it's not like you're
> at school messing about.

Probably. But that's not my department. From *my* chair, the issue is
that only certain individuals should even be able to do that in the
first place.
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
>> Geez, what sort of people have you got working there?  Surely that sort
>> of behaviour demands some sort of official warning, it's not like you're
>> at school messing about.
>
> Probably. But that's not my department. From *my* chair, the issue is that
> only certain individuals should even be able to do that in the first
> place.

Oh right, good luck, next you'll have to stop him from pressing the reset
button, then from turning the machine off at the mains, then from unplugging
the network cable etc.  It quickly becomes impossible to stop someone who is
set on causing disruption, far better to give them an "incentive" not to do
it - like "oi stop this behaviour or you'll be sacked" :-).
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
scott wrote:
>>> Geez, what sort of people have you got working there?  Surely that
>>> sort of behaviour demands some sort of official warning, it's not
>>> like you're at school messing about.
>>
>> Probably. But that's not my department. From *my* chair, the issue is
>> that only certain individuals should even be able to do that in the
>> first place.
>
> Oh right, good luck, next you'll have to stop him from pressing the
> reset button, then from turning the machine off at the mains, then from
> unplugging the network cable etc.  It quickly becomes impossible to stop
> someone who is set on causing disruption, far better to give them an
> "incentive" not to do it - like "oi stop this behaviour or you'll be
> sacked" :-).

Well, AFAIK, the guy isn't *trying* to cause problems, he's just a bit
overkeen. He probably doesn't realise that logging somebody off actually
terminates any programs they might have running (e.g., the control
software for the robotics that inject the samples into the system).
Turning the PC off at the mains, however, is "obviously" a Bad Thing.

More importantly, it's a Bad Thing that I obviously have no power to
prevent - so if it happens, it won't be my problem! :-D
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
> overkeen. He probably doesn't realise that logging somebody off actually
> terminates any programs they might have running (e.g., the control
> software for the robotics that inject the samples into the system).

Can't you just tell him that then, instead of having to spend time locking
down your system.  Maybe there is a situation one day where someone
genuinely needs to log off another user and you're not available?
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |
| |
|
|
scott wrote:
>> overkeen. He probably doesn't realise that logging somebody off
>> actually terminates any programs they might have running (e.g., the
>> control software for the robotics that inject the samples into the
>> system).
>
> Can't you just tell him that then, instead of having to spend time
> locking down your system.  Maybe there is a situation one day where
> someone genuinely needs to log off another user and you're not available?

...which is why a small set of other people are "supposed" to have this
power in addition to me.

But the set of people needing to restart services is far larger than the
set of people who should have log-off powers.
Post a reply to this message
|
|
| |
| |
|
|
|
|
| |